Don’t let human hackers disorient your employees.
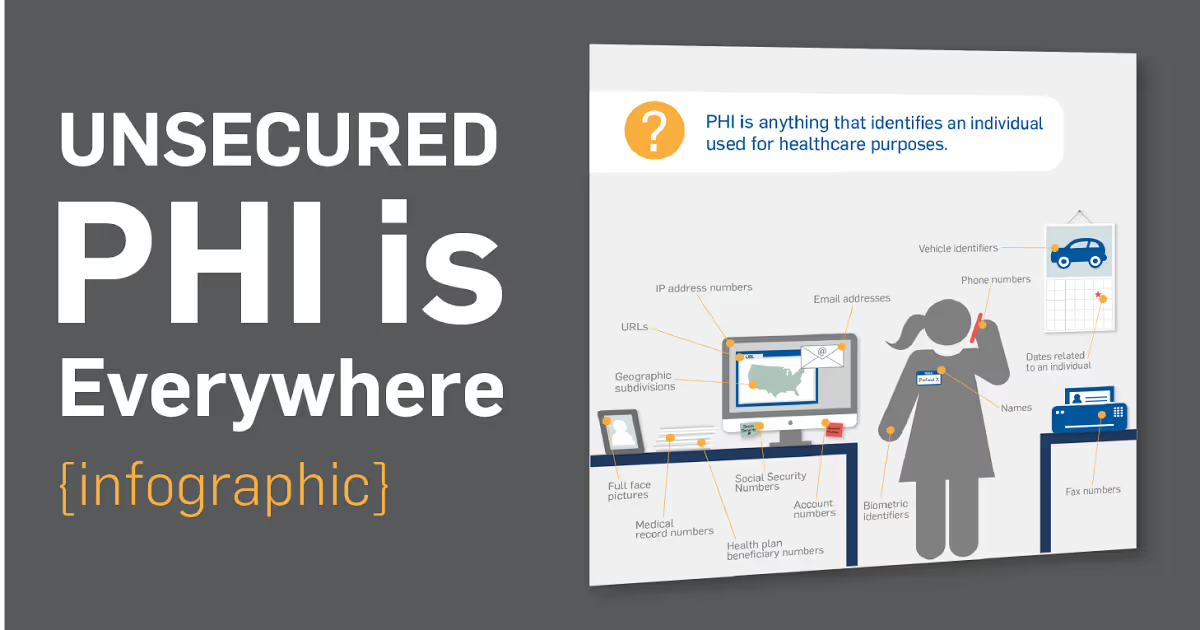
The unprotected PHI problem is easy to fix, but it must start with you.
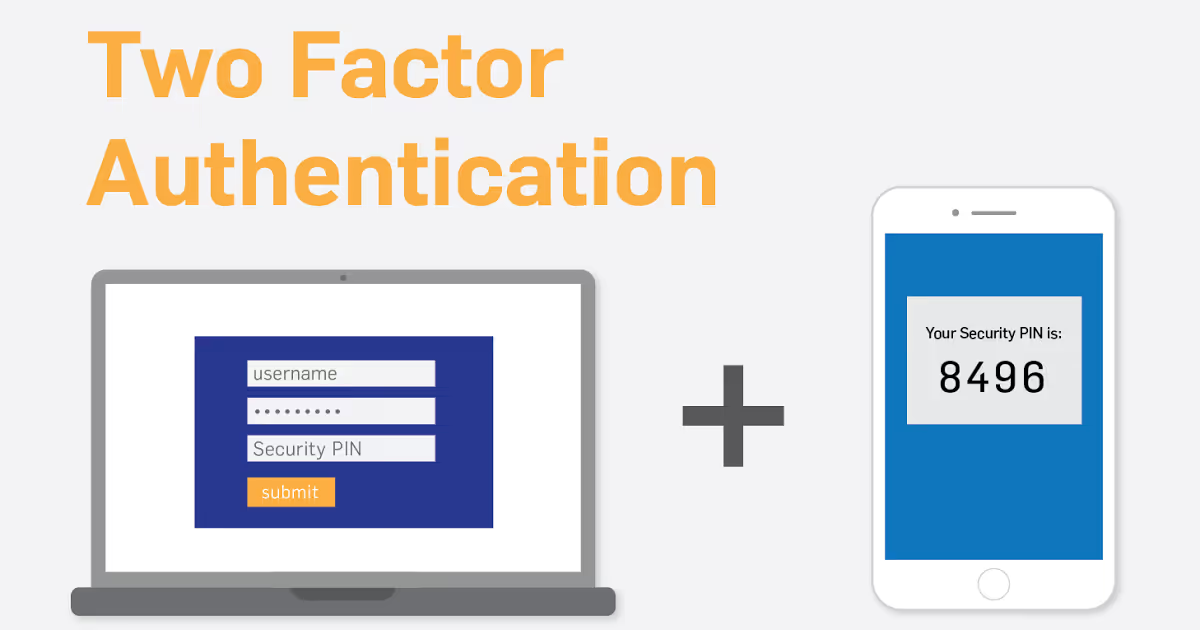
Is two-factor authentication perfect? No, but it does make a hacker’s job more difficult.
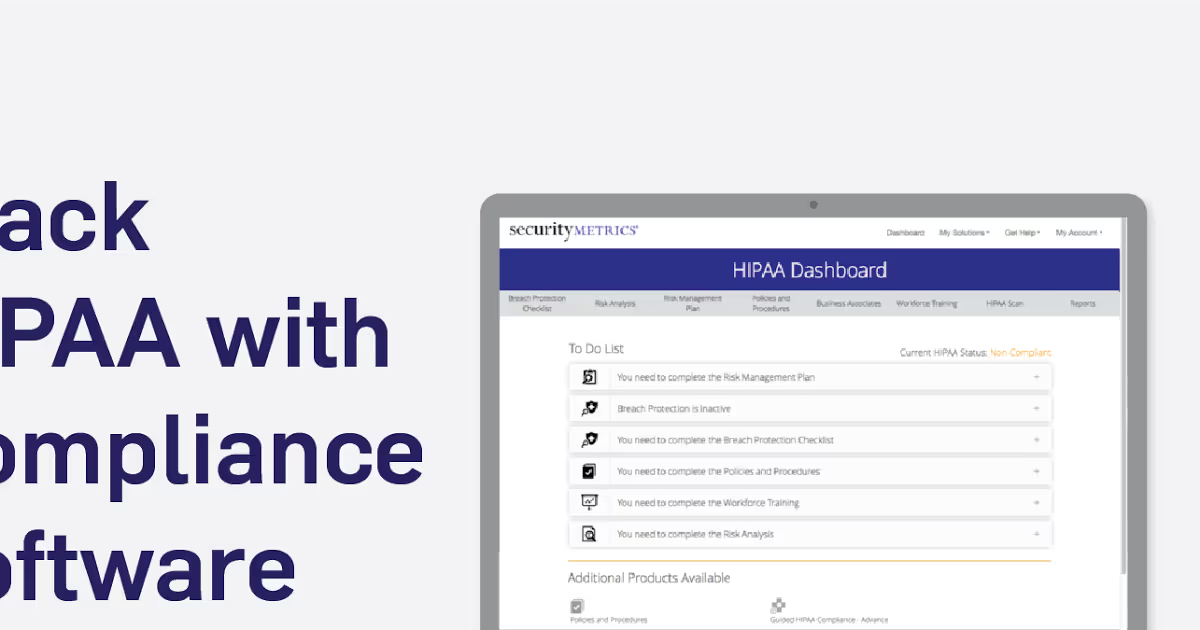
This HIPAA compliance software is easy to update and doubles as a documentation tool.
Log management and regular log review could help identify malicious attacks on your system.
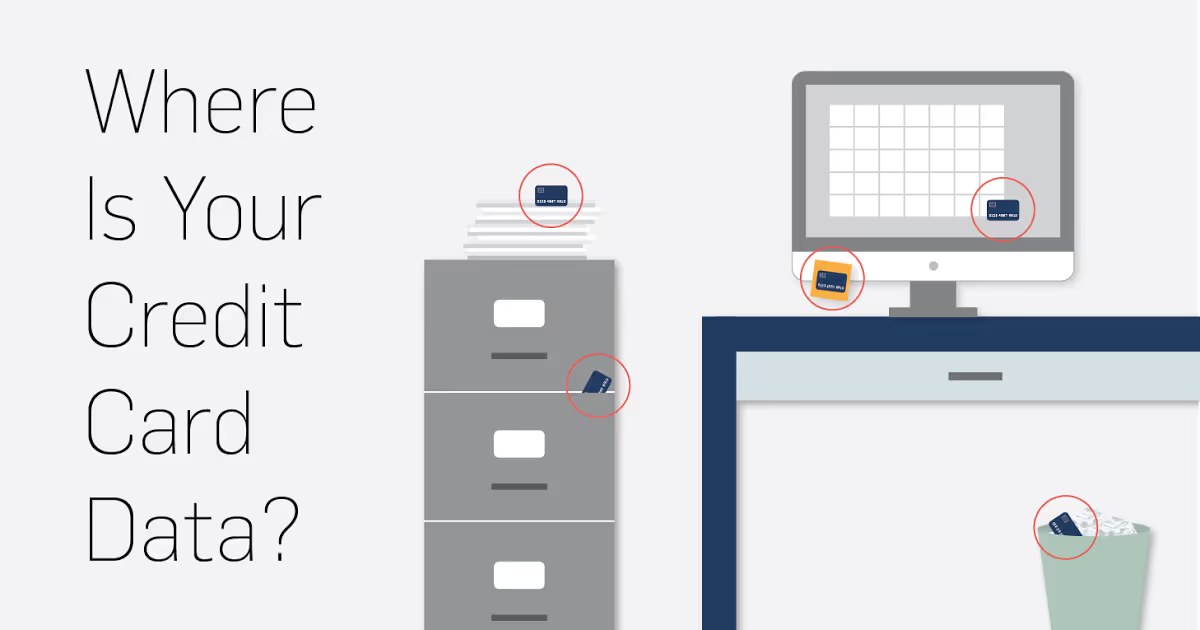
Unencrypted credit card data is hiding on your network
Hackers don’t care who you are. They just care how rich you can make them.
Hopefully this incident helps both healthcare to remember the fragility of patient data protection.
Not all approved scanning vendors are created equal
It’s simple to protect patient data from malware with the right tools, controls, and people in place.
Find out the most-read PCI DSS compliance and data security posts.
Remote access technology has been turned against us by cybercriminals.
Depending on a few factors, cyber insurance premiums can cost from $650 to easily over $120,000 annually.
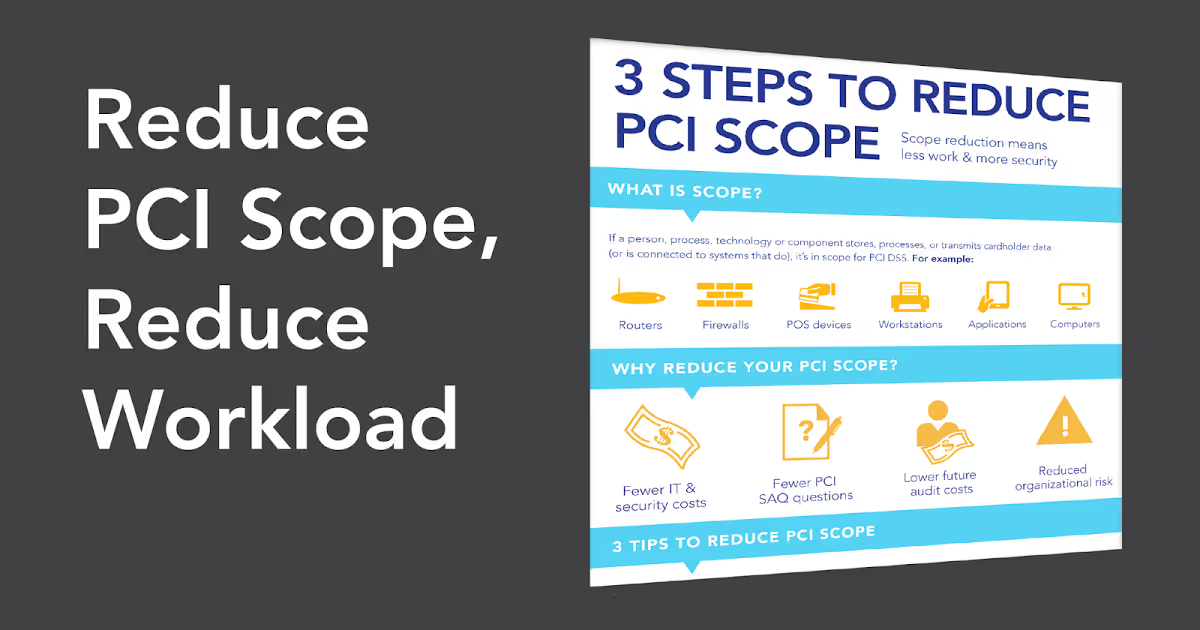
The way you handle emailing credit card info might just change your scope for PCI DSS compliance.
Those exorbitant fines are why cyber breach insurance exists.
Healthcare entities must be proactive about protecting sensitive data across their organization.
An industry-recognized methodology must be used when conducting a penetration test.


